How To Completely Disable ufw in Linux Ubuntu Mint Debian
This is for the situation that you're doing other things that may conflict or have your own custom rules and ufw keeps overriding iptables.
A lot of guides don't work, and even ufw reset does not work, because it still leaves the old ufw chains.
Here is what works to disable ufw completely
systemctl stop ufw
systemctl disable ufw
ufw disable
rm -f /etc/ufw/*
iptables -F
Now run this script to finish the job
This script will delete all of the old ufw chains.
for chain in `iptables -L|grep ufw|awk '{print $2}'`; do

iptables -X $chain

done
Do this in case:
Sometimes the default iptables policy for FORWARD, OUTPUT, INPUT will be drop
iptables --policy FORWARD ACCEPT
iptables --policy INPUT ACCEPT
iptables --policy OUTPUT ACCEPT
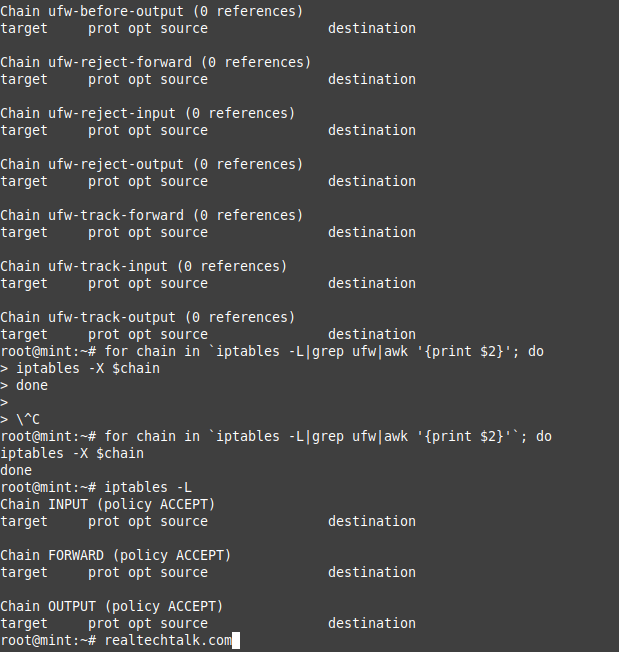
We can see all the old chains below before running the script and then after the script they are all deleted.
Tags: